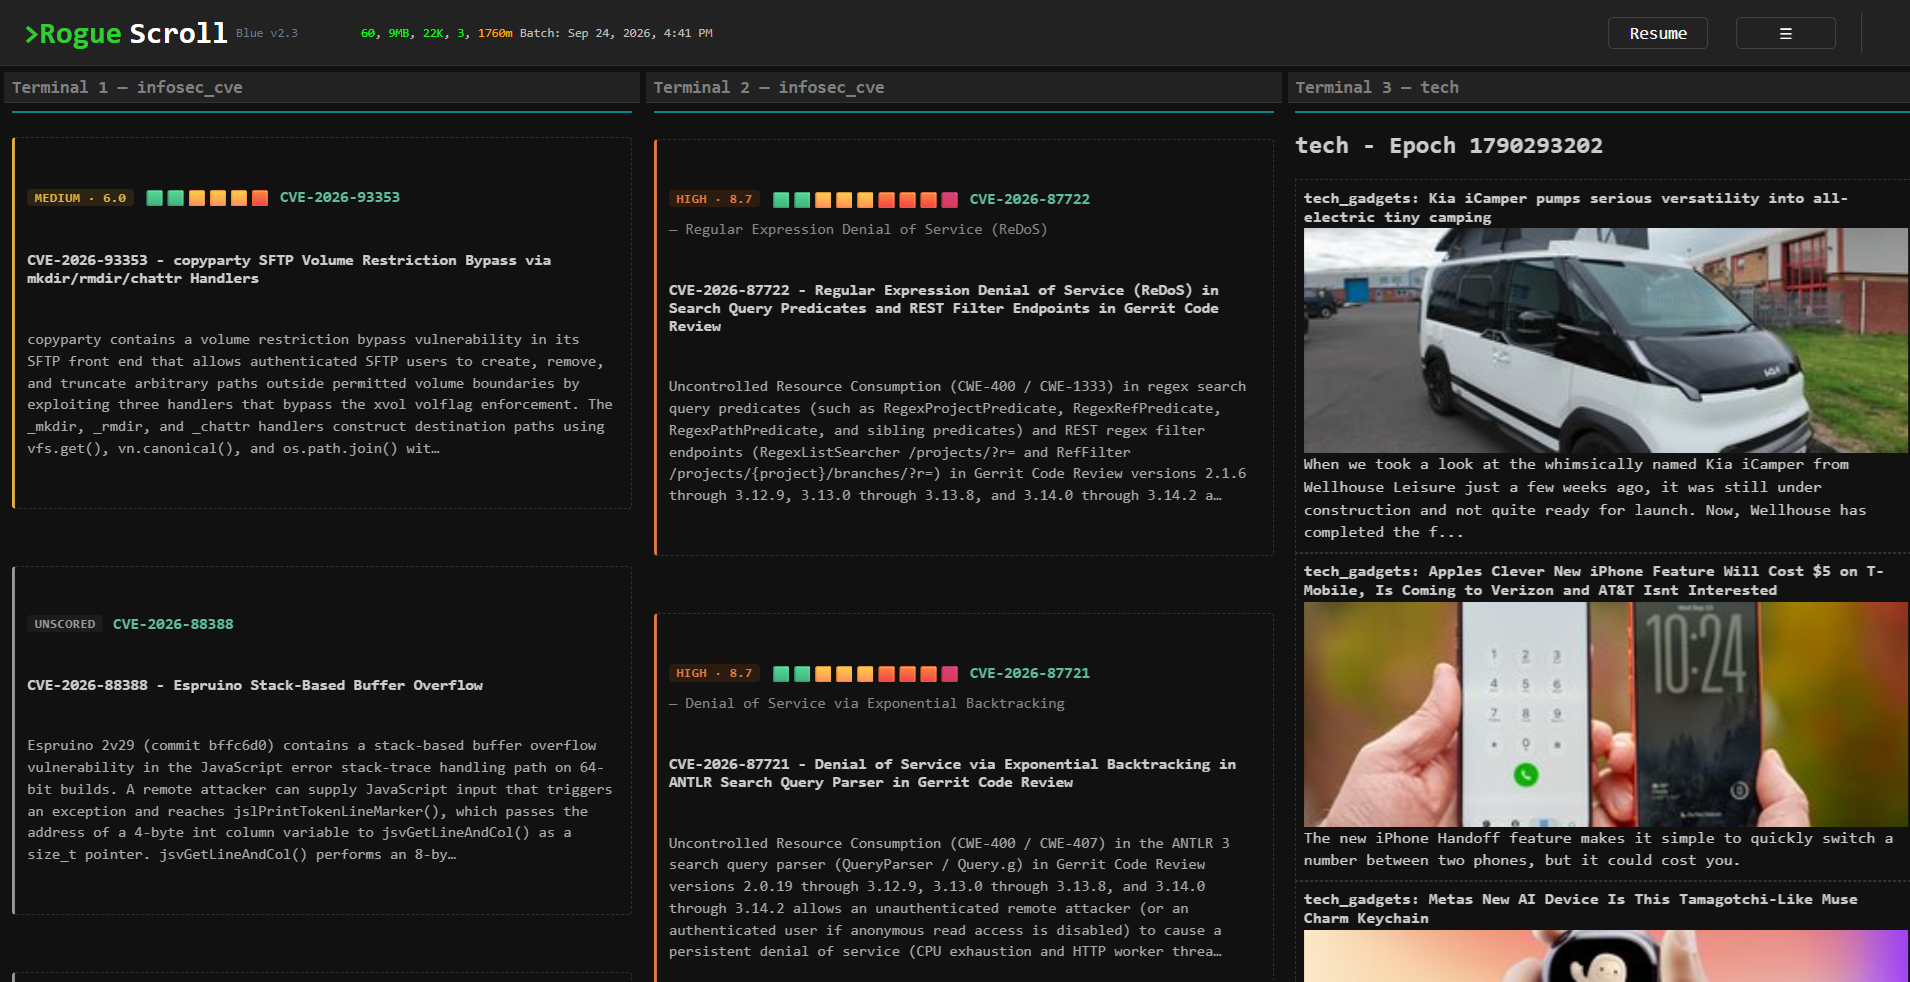
Built an ambient CVE feed for my second monitor — useful or information overload?
Source Reddit Cybersecurity
Discussion
This content describes an experimental ambient CVE feed display designed to run on a second monitor, continuously scrolling recent CVE information alongside other technology feeds. The purpose is to provide peripheral awareness of new vulnerabilities without active monitoring. The post seeks community input on useful complementary data such as CISA KEV, EPSS, known exploitation status, or vendor/product filters. There is no indication of a specific vulnerability or active threat in this content.
r/cybersecurity (opens in a new tab)u/RobertLawsonVaughn0 points0 comments
I've been experimenting with an ambient information display called RogueScroll, designed to sit on a second monitor while I work.
This configuration continuously scrolls recent CVEs across two terminals, with a general technology feed in the third. The idea isn't to actively monitor it — it's more like peripheral awareness. Something catches your eye, then you investigate.
I'm curious how security folks would configure something like this.
What would you want alongside the CVE data? CISA KEV? EPSS? Known exploitation? Vendor/product filters? Something else?
Screenshot: https://roguescroll.com/images/roguescroll.com_infosec_CVE.png